How AegisAI stops vendor payment fraud
Episode details and transcript
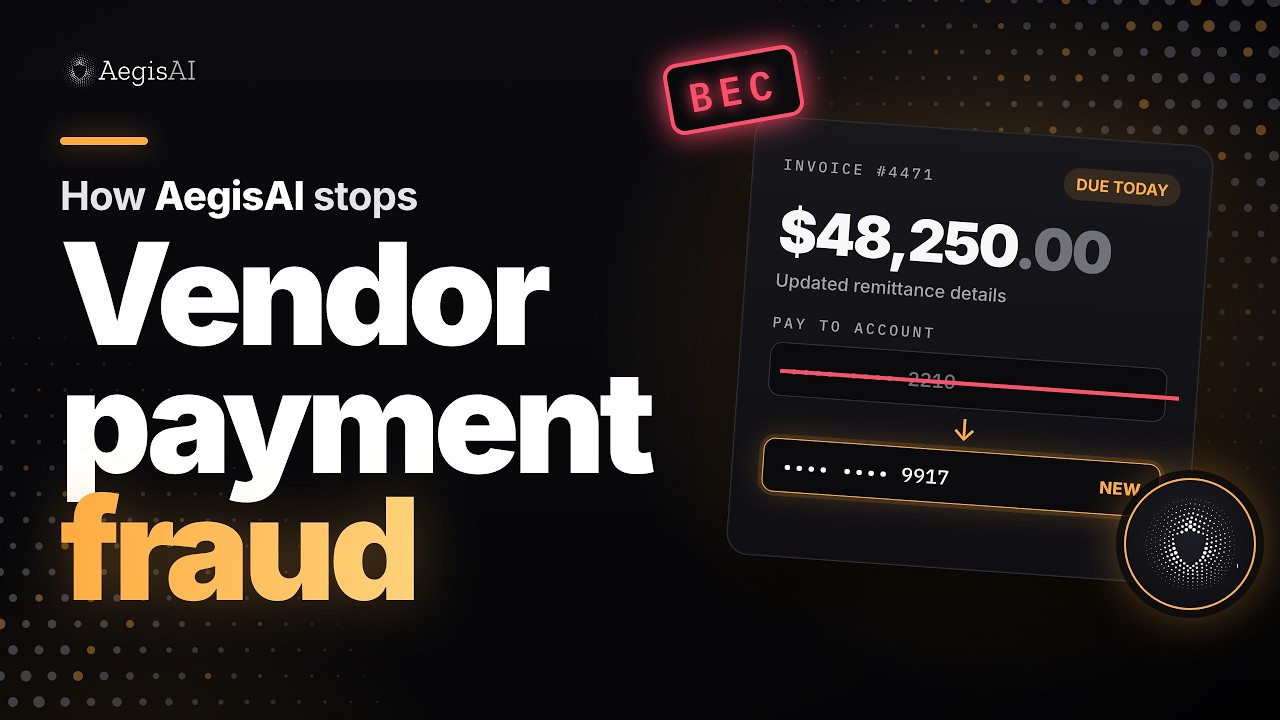
A 48 second animated walkthrough of a vendor payment fraud attempt, the business email compromise (BEC) attack that redirects a supplier payment. It shows the four steps AegisAI takes: Connect, Investigate, Protect, Extend. Illustrative example; names and details are fictional.
A reply inside a real invoice thread asks to update remittance details. The sender's domain is one letter off a real supplier's. Here is how AegisAI catches it.
01 Connect
AegisAI connects to Microsoft 365 or Google Workspace, mail and directory, by API, out of band.
02 Investigate
Agents flag a first email from this sender, a request to change bank details, a policy that payment changes need a callback, and a reply-to that differs from the sender. The verdict: business email compromise. The email is quarantined and the finance team is alerted.
03 Protect
Inbound email security and BEC attack prevention stop attacks that pass SPF, DKIM and DMARC.
04 Extend
The email is replayed to the 3 people in accounts payable as training.
Illustrative example. Names and details are fictional.