How Mirage2FA bypasses Microsoft 365 MFA with stolen session cookies
Yes, attackers bypass Microsoft MFA. The Mirage2FA AiTM kit relays the real login and takes the session cookie the moment MFA clears. Here is how it works.
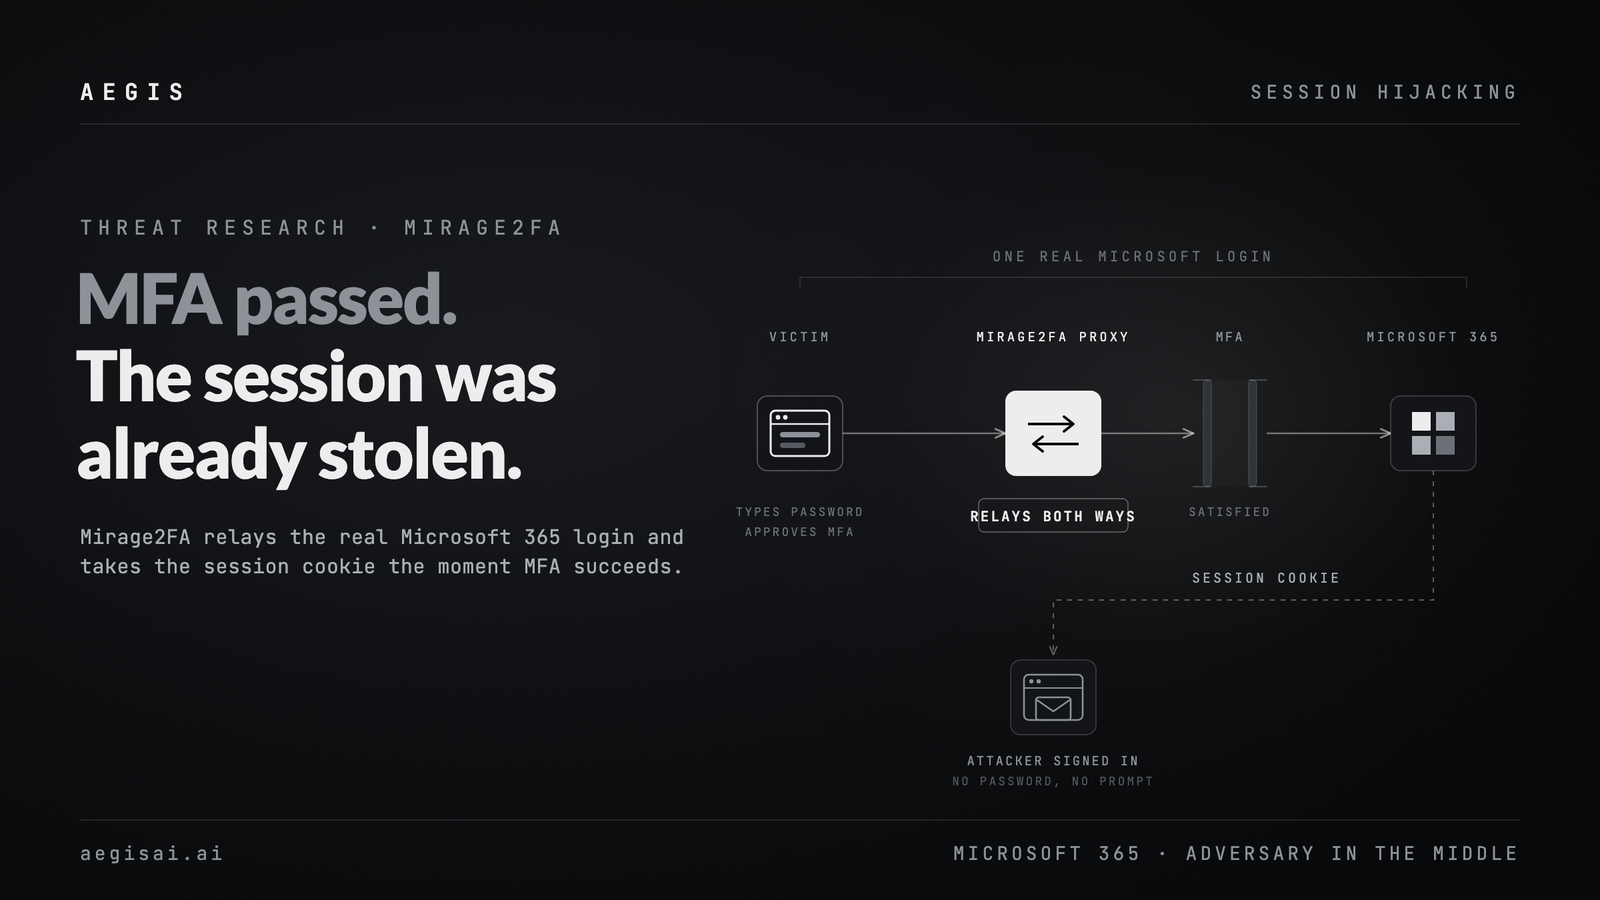

A phishing kit called Mirage2FA has targeted at least 4,532 organizations across the US and EU since 2024, and it surged in August 2026. It uses no new exploit. It defeats multi factor authentication by proxying the victim's live login and taking the session cookie the moment MFA clears. ANY.RUN, which tracked the campaign through its sandbox platform, logged more than 9,000 session theft events and estimates 48% of the targeted email addresses were likely compromised. Roughly 63.7% of targeted domains sit in the United States, with technology, manufacturing, and education among the hardest hit sectors.
Can someone bypass Microsoft MFA?
Yes, and Mirage2FA shows how routine it has become. An adversary in the middle kit does not need to defeat the second factor. It sits between the victim and Microsoft, lets the real login and the real MFA prompt succeed, and takes the session cookie Microsoft issues at the end. With that cookie, the account is reachable without a password and without a prompt.
How Mirage2FA defeats MFA without breaking it
Mirage2FA is an adversary in the middle, or AiTM, phishing as a service kit. Instead of harvesting a static password and hoping to reuse it later, the kit proxies the victim's live login session against Microsoft 365. As the target enters credentials and completes MFA, the kit captures both the password and the resulting session cookie in real time. That cookie is what makes the account usable without a password at all. Once an attacker holds it, they can reach Microsoft 365 and any SSO connected service the same way the legitimate user would, with no second authentication prompt.
Older credential phishing relies on replay: an attacker steals a password, tries to log in later, and the second factor stops them. Mirage2FA never attempts replay. It rides along inside the original, already authenticated session, so the control built to stop the attack never fires.
AiTM phishing at commercial scale
AiTM kits are not new. What the numbers show is how far the model has scaled as a commercial operation. Over 9,000 compromise events across 4,532 organizations takes a kit built for repeatable, high volume use, sold or shared widely enough to reach companies in the US, EU, India, Singapore, the UK, Canada, Saudi Arabia, and South Africa.
Static, rule based email filters catch known bad senders, domains, and message signatures. An AiTM proxy page can be stood up on new infrastructure faster than those rules update, and the resulting traffic looks like a real login to a real Microsoft page, so signature based detection has little to work with.
How to defend against session cookie theft
MFA still stops replay attacks, which is most of what it was built to do. It is one checkpoint, and Mirage2FA shows how routinely attackers now walk through it. Security teams should treat session cookie theft as a threat category separate from password theft, with its own detection and response plan:
- Session length and re-authentication policies that limit how long a stolen cookie stays useful.
- Conditional access rules that flag improbable travel, new device fingerprints, and token use from unexpected networks.
- Monitoring for the anomalous sign-in patterns AiTM sessions produce, including sign-ins that skip the interactive MFA step entirely.
For any team running Microsoft 365, the practical next step is to audit how fast a stolen session cookie would get noticed today.
Where email security fits
The proxy page still has to be delivered, and email is how these campaigns reach their targets. That makes the link, not just the sender, the thing worth reasoning about. AegisAI's agents evaluate the message and the destination it points to together, and pull a malicious message out of mailboxes before users see or click it. Read more on how we approach inbound email security and BEC attack prevention, or book a demo to see it run against your own traffic.
Related posts
More from the AegisAI blog.