Operation Social Undertow: A Phishing Campaign Spoofing the Social Security Administration
Threat actors deploy SimpleHelp RAT via sophisticated SSA phishing.
Executive Summary
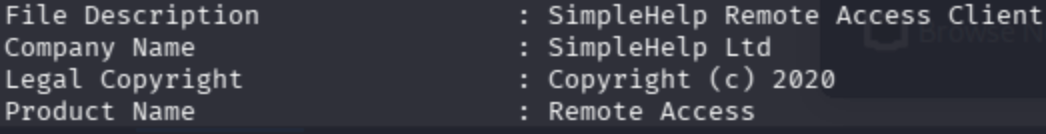
The AegisAI Threat Intelligence team has been monitoring an active and sophisticated phishing campaign, dubbed Operation Social Undertow, that is leveraging a network of compromised WordPress sites to help deliver a remote access tool. Characterized by broad-based, indiscriminate targeting, this campaign poses a widespread threat that has been observed impacting enterprise companies across multiple sectors. Discovered on January 7, 2026, the campaign’s primary objective is the deployment of a SimpleHelp Remote Access Client, likely to facilitate data exfiltration or subsequent compromise events.
Key Findings
| Metric | Detail |
|---|---|
| Discovery Date | January 7, 2026 |
| Campaign | Phishing via compromised WordPress instances. |
| Primary Target | Broad-based, indiscriminate targeting via spoofing a message from the Social Security Administration. |
| Payload | SimpleHelp Remote Access Client (.exe file). |
| Sophistication | High. Utilizes Cloudflare TLS fingerprinting to evade automated scanning and analysis of attacker-controlled domains. |
Technical Analysis
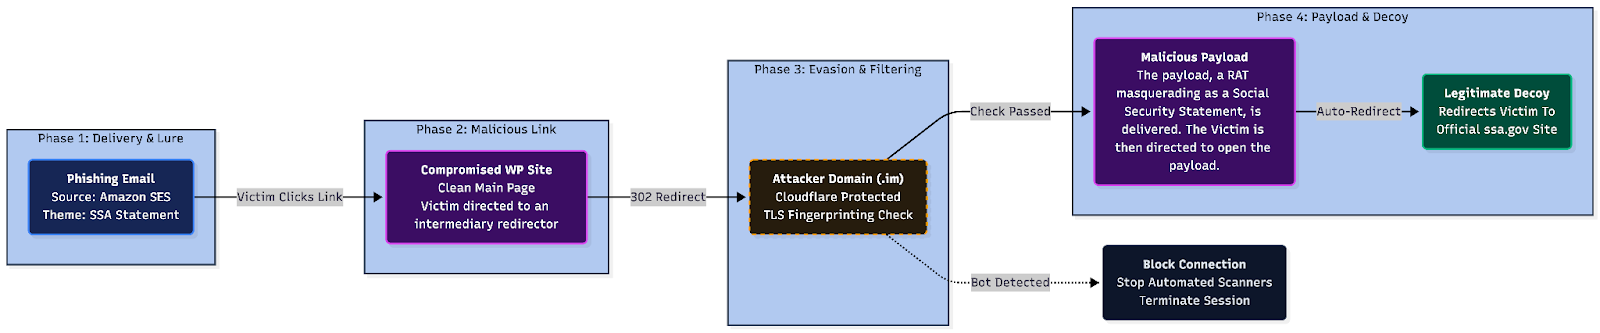
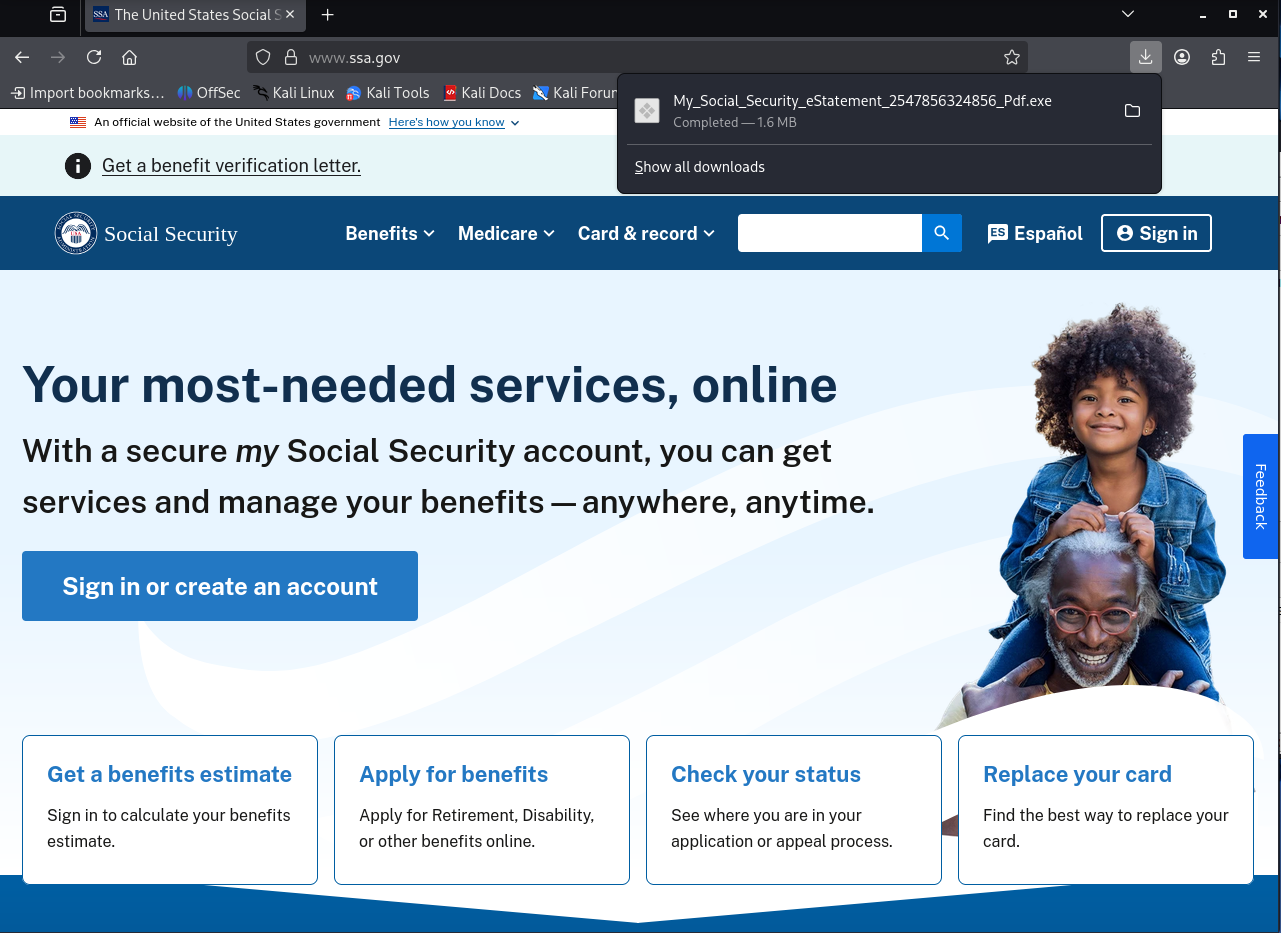
Unlike traditional credential harvesting phishing kits, this campaign's primary objective is to deliver a malicious executable file (My_Social_Security_eStatement_..._Pdf.exe) to the victim's device using a "drive-by download" technique, followed by a redirection to the legitimate SSA website to minimize suspicion. The attack follows a multi-stage redirection and execution flow:
- Phishing Email
- Initial Entry Vector (Compromised Site)
- Malicious Landing Page
- Payload Delivery
- Decoy Redirection
1. Phishing Email
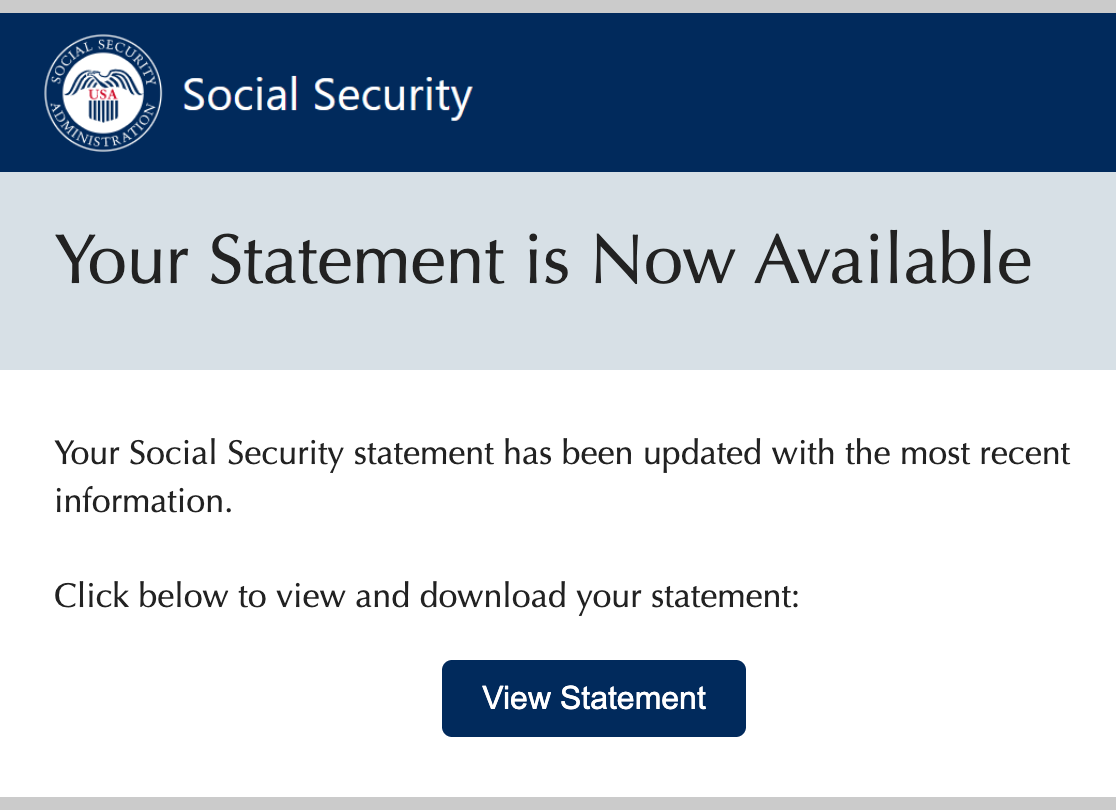
The emails are sent from compromised users from trusted domains and are designed to mimic legitimate Social Security Administration communications, using subject lines such as “Your Statement Is Ready for Viewing” or “Discover Your Updated Benefits.”
A. Delivery Status: These emails generally don't get classified as spam by popular email clients, and typically pass all authentication headers.
B. Automation: Emails were sent using Amazon SES, suggesting a high level of campaign automation.
C. Infection Flow: Users are lured to click a malicious link embedded in the body, which initially directs them to a compromised WordPress site.
2. Initial Entry Vector (Compromised Site)
The victim initiates the infection flow by clicking a link that leads to a compromised WordPress site, a technique often favored by threat actors as tenured sites have a higher likelihood of evading spam detection.
A. URL: hxxps[://]buntai[.]com/wp-includes/Fubh3trgf[.]php?{victim_email}
B. Redirect: After the cookie pass (containing the victim's IPv6 address) is set, the server serves the malicious landing page. The IPv6 address is being tracked by the attacker controlled domain to check if users have already visited the link, whereas the {victim_email} is used for logging/tracking by the attacker at this stage. The {victim_email} is not passed to the landing page, because the final payload (Malware) does not require user context/pre-filling.
3. Malicious Landing Page
The victim lands on an attacker controlled domain (ex: hxxps[://]ss-a-ref[.]im/VR/), a spoofed page designed to mimic a legitimate Login.gov / SSA intermediary page.
A. Infrastructure: Proxied behind Cloudflare. Cloudflare is used to actively deny access to spoofed user agents, preventing traditional automated threat analysis and sandboxing.
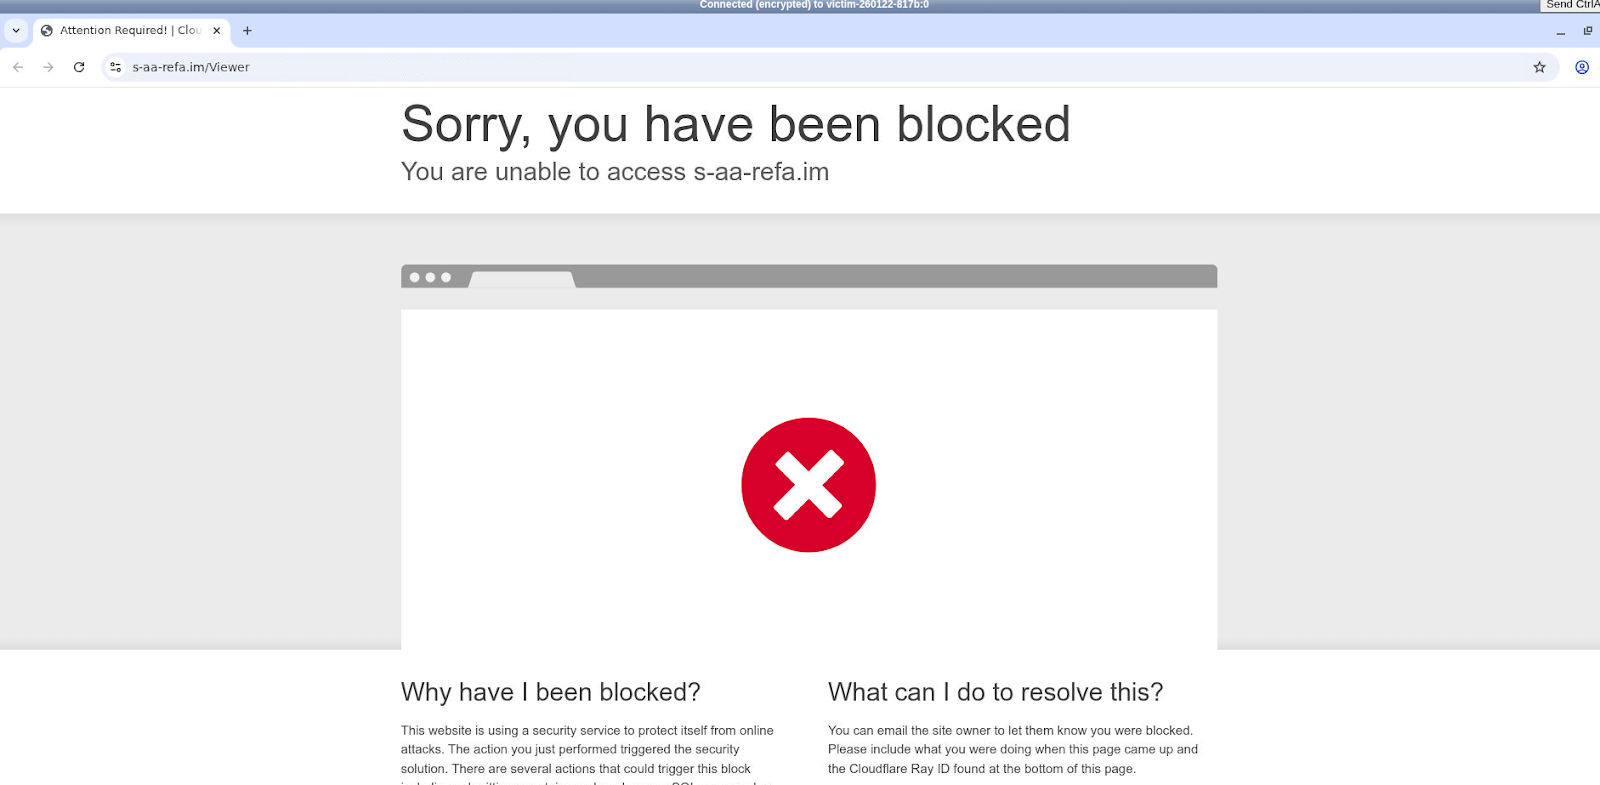
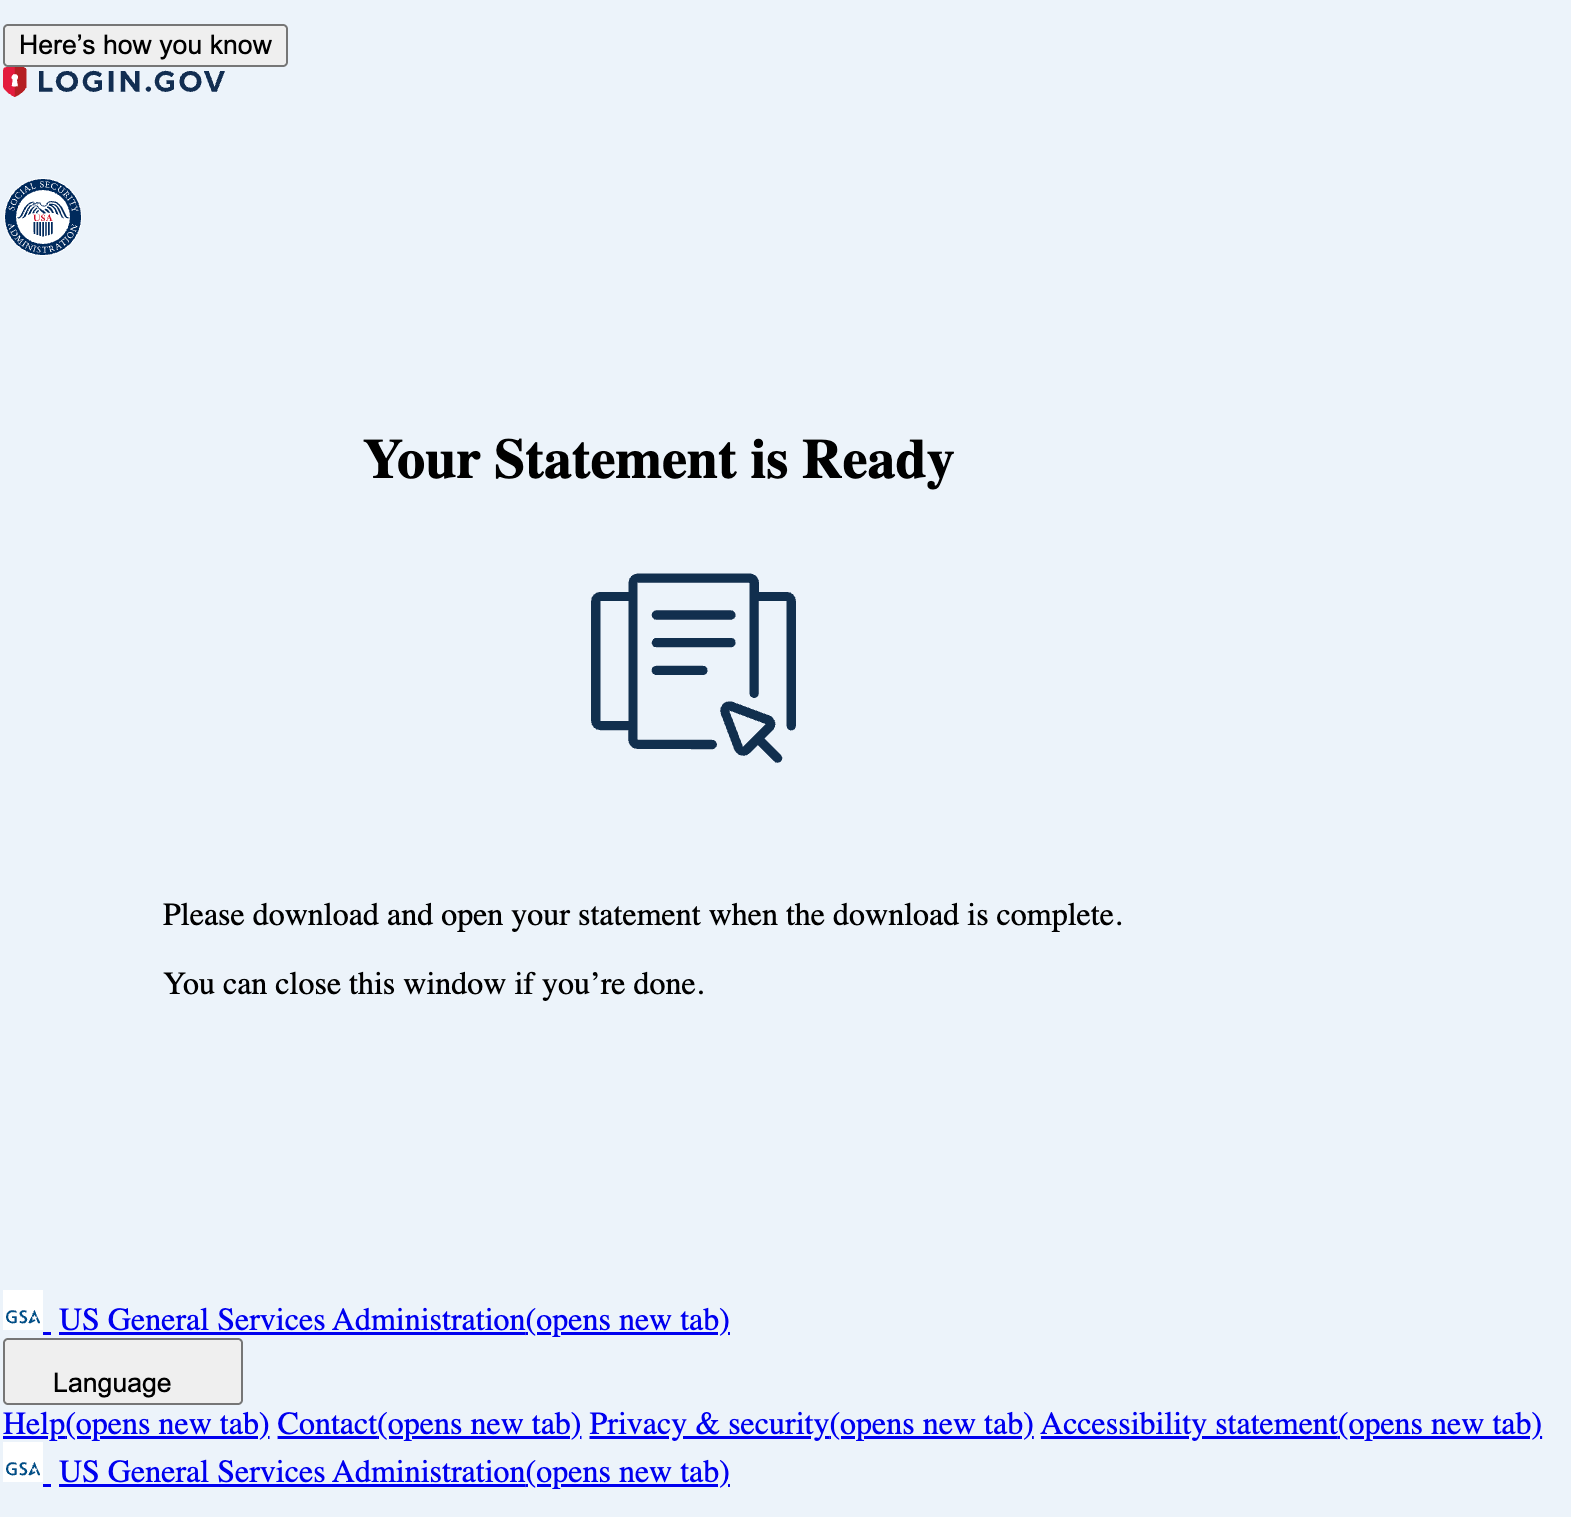
B. Visuals: The page typically displays a message like "Check your email" or "Your Statement is Ready" and directs the victim to open the payload, and "hotlinks" CSS and JS assets directly from secure.login.gov in an attempt to spoof the page. Despite linking real assets, the page does not render correctly. The reliance on external assets combined with amateur inline styles (e.g., hardcoded margins) and potentially conflicting CSP (Content Security Policy) headers from the legitimate site causes the layout to break, serving as a potential visual warning to observant victims.
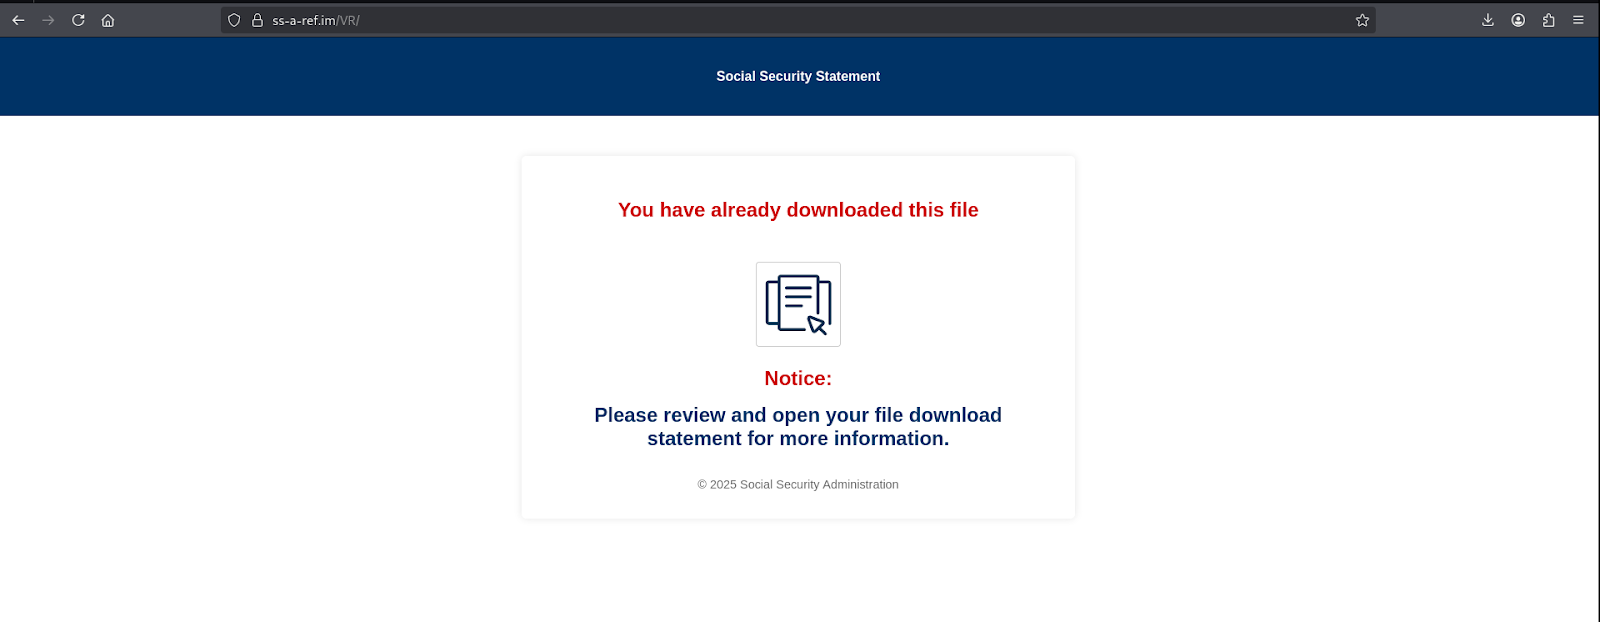
C. IPv6 Tracking: If a tracked IPv6 visits the same attacker controlled domain, the following message is displayed:
4. Payload Delivery
A javascript function automatically triggers the download of the payload via:
A. Payload URL: hxxps[://]seymu[.]net/public/[.]BT/My_Social_Security_eStatement_2547856324856_Pdf[.]exe
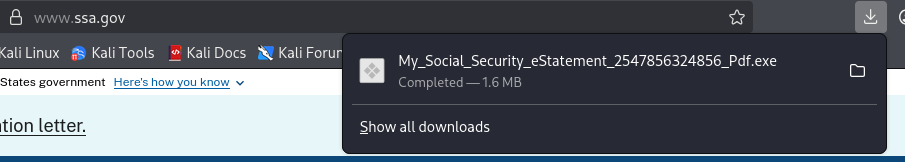
B. Details: The payload is a RAT (Remote Access Trojan) masquerading as a Social Security statement.
5. Decoy Redirection
After initiating the download and a short delay, the script redirects the user's browser to the legitimate https://www.ssa.gov. The user lands on the real SSA homepage, likely believing the download was a legitimate part of the process.
Indicators of Compromise (IOCs)
Organizations are strongly advised to block the following IOCs immediately
| Type | Indicator |
|---|---|
| Known Hashes of Payload (SHA-256) |
2a3f693dc00c01ae5f1b654bc068eea5c9463af30ba082584a74677267b5120f
↗ View on Virustotal |
| Known Attacker Controlled Domains (TLD: .im) |
ss-a-ref[.]im s-aa-refa[.]im Irs-ref[.]im irsw-rea[.]im |
| Known Compromised Sender Domains |
mocktrade-scheduler[.]com aurycloth[.]com 2bsip[.]com brasaf-sa[.]com idpe[.]org[.]uk jayanetwork[.]in nsgrafica[.]ao n4kitchenhire[.]co[.]uk tsrtk[.]com sellescom[.]com[.]br |
| Known Compromised WordPress Instances |
xaynhadanang[.]net syscarelimited[.]com theteafaq[.]com shellstarrealty[.]com suiterobot[.]com brumateus[.]com yourdestany[.]com wartakadin[.]com buntai[.]com kenyacrash[.]com reflectphotoelegance[.]com cms[.]ultim8e[.]com cibarrap[.]com hackmedia[.]net amanatproperty[.]com owais-al-hashimi[.]com arabicwatch[.]net app[.]fyvello[.]com garagecoatingpros[.]com villageofviscount[.]ca eduka[.]themejr[.]net ommatrucking[.]com demo[.]kamleshyadav[.]com tamilink[.]org[.]uk settingserver[.]com certified-mail-envelopes[.]com dev[.]cxplab[.]com doel-bereik[.]com naooko[.]com aurelianconsultingllc[.]com kmansin[.]org lolive[.]skillup[.]com[.]br meet[.]believersconnect[.]org bollywoodmash[.]coinbitwallet[.]com capitalguidex[.]com bedigitalproject[.]com malecelebsleaked[.]com endzone247[.]com dars360[.]com indialive[.]net msgforlove[.]com 3000-club[.]com mommytaste[.]com tervalidasi[.]com mdsservicescontrols[.]com getmediawise[.]com discretmature[.]net microninfo[.]com api[.]ssstik[.]net test1[.]thanglon[.]com epikshocks[.]com adronestates[.]com castlemilebrampton[.]com suzon-suzette[.]fr scienceinfotech[.]com venturas[.]newclientdemo[.]com dietamais[.]com[.]br greeninovation[.]com quodb[.]com misbookrights[.]com gold-seeds[.]net vps133808[.]conectemos[.]com sitevader[.]com abibimanmall[.]com naptecprecision[.]com hanoijeeptours[.]com helpmom[.]net cfkb[.]shipsmart242[.]com capitalimport[.]info s1[.]financebg[.]com tostapane[.]net rakindustrialsupplies[.]com blog[.]cargeeks[.]net fremontpiperepairpros[.]com fresnocprclasses[.]com febet[.]partners |
Related posts
More from the AegisAI blog.